Transcribed
Course 39 - NodeJS Security Pentesting and Exploitation | Episode 3: Hardening Code and Preventing Attacks
Jul 9, 2026 ·
18m 59s
Download and listen anywhere
Download your favorite episodes and enjoy them, wherever you are! Sign up or log in now to access offline listening.
Course 39 - NodeJS Security Pentesting and Exploitation | Episode 3: Hardening Code and Preventing Attacks
This automatic transcript is brought to you by
Sounder.AI
This is an automatically generated transcript. Please note that complete accuracy is not guaranteed.
Description
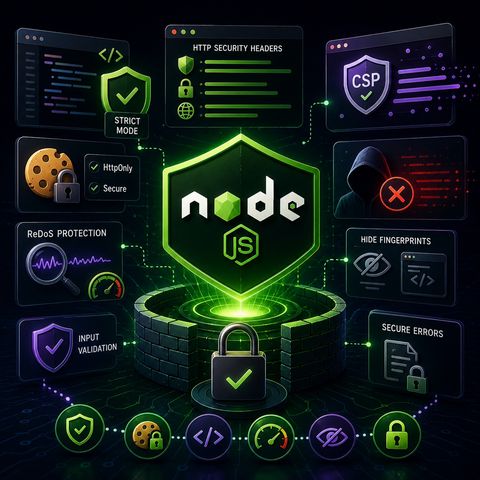
In this lesson, you’ll learn about: securing Node.js applications through safe coding practices, HTTP security headers, ReDoS protection, and preventing information disclosure1. Secure Coding in Node.js🔹 Key idea: Secure Node.js...
show more
In this lesson, you’ll learn about: securing Node.js applications through safe coding practices, HTTP security headers, ReDoS protection, and preventing information disclosure1. Secure Coding in Node.js🔹 Key idea:
Secure Node.js applications require strict control over execution context and defaults.🔹 Strict Mode
Strict mode reduces “silent” security bugs caused by sloppy scope handling2. HTTP Security Headers (Defense Layer)🔹 Tool:
Helmet.js🔹 What it does:
Automatically sets important security headers in Express apps.🔹 Key headers it manages:
Headers act as a browser-level security shield3. Secure Cookies🔹 Important flags:
Even if XSS happens, HttpOnly cookies cannot be stolen via JS4. Regular Expression Denial of Service (ReDoS)🔹 What it is:
A performance attack exploiting bad regex patterns🔹 How it works:
A “valid” input can still be a computational attack5. Preventing ReDoS Attacks🔹 Strategies:
Security includes performance safety, not just access control6. Information Disclosure Risks🔹 Problem:
Attackers learn stack/framework details from responses7. Hiding Technology Fingerprints🔹 Disable default headers
Default cookies like connect.sid reveal framework usage🔹 Fix:
Small naming details can expose backend stack9. Custom Error Handling🔹 Problem:
Default errors expose:
Errors should help users—not attackers10. Big PictureYou are learning how to:👉 Harden Node.js applications at multiple layers
👉 Prevent CPU-based DoS attacks (ReDoS)
👉 Reduce information leakage from HTTP responses
👉 Apply production-grade security middlewareMental ModelStrict mode → secure headers → safe cookies → regex safety → hidden fingerprints → controlled errors → hardened application surface
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
show less
Secure Node.js applications require strict control over execution context and defaults.🔹 Strict Mode
- Enables safer JavaScript execution
- Prevents accidental global variables
- Forces explicit variable declarations
Strict mode reduces “silent” security bugs caused by sloppy scope handling2. HTTP Security Headers (Defense Layer)🔹 Tool:
Helmet.js🔹 What it does:
Automatically sets important security headers in Express apps.🔹 Key headers it manages:
- Content Security Policy (CSP) → blocks malicious scripts
- HTTP Strict Transport Security (HSTS) → forces HTTPS
- XSS Protection headers → reduces injection risks
Headers act as a browser-level security shield3. Secure Cookies🔹 Important flags:
- HttpOnly
- Blocks JavaScript access to cookies
- Secure
- Ensures cookies are only sent over HTTPS
Even if XSS happens, HttpOnly cookies cannot be stolen via JS4. Regular Expression Denial of Service (ReDoS)🔹 What it is:
A performance attack exploiting bad regex patterns🔹 How it works:
- Complex input causes exponential backtracking
- CPU usage spikes
- Server becomes unresponsive
- Email validation
- Input sanitization
A “valid” input can still be a computational attack5. Preventing ReDoS Attacks🔹 Strategies:
- Avoid overly complex regex patterns
- Limit input length
- Use safe validation libraries
- Benchmark regex performance
Security includes performance safety, not just access control6. Information Disclosure Risks🔹 Problem:
Attackers learn stack/framework details from responses7. Hiding Technology Fingerprints🔹 Disable default headers
- Remove X-Powered-By
- Hide framework identity
- Default headers reveal backend technology
- Removing them reduces attack surface visibility
Default cookies like connect.sid reveal framework usage🔹 Fix:
- Rename cookies
- Customize session identifiers
Small naming details can expose backend stack9. Custom Error Handling🔹 Problem:
Default errors expose:
- Stack traces
- File paths
- Internal logic
- Use production-safe error handlers
- Return generic messages only
Errors should help users—not attackers10. Big PictureYou are learning how to:👉 Harden Node.js applications at multiple layers
👉 Prevent CPU-based DoS attacks (ReDoS)
👉 Reduce information leakage from HTTP responses
👉 Apply production-grade security middlewareMental ModelStrict mode → secure headers → safe cookies → regex safety → hidden fingerprints → controlled errors → hardened application surface
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
Information

Copyright 2026 - Spreaker Inc. an iHeartMedia Company

Comments