Transcribed
Course 37 - Building Web Apps with Ruby On Rails | Episode 14: From Basic HTTP to JWT Authentication
Jun 27, 2026 ·
19m 33s
Download and listen anywhere
Download your favorite episodes and enjoy them, wherever you are! Sign up or log in now to access offline listening.
Course 37 - Building Web Apps with Ruby On Rails | Episode 14: From Basic HTTP to JWT Authentication
This automatic transcript is brought to you by
Sounder.AI
This is an automatically generated transcript. Please note that complete accuracy is not guaranteed.
Description
In this lesson, you’ll learn about: securing APIs in Rails, authentication strategies, and building a stateless authorization system1. Why API Security MattersUsing Ruby on Rails APIs:🔹 Problem: - APIs are...
show more
In this lesson, you’ll learn about: securing APIs in Rails, authentication strategies, and building a stateless authorization system1. Why API Security MattersUsing Ruby on Rails APIs:🔹 Problem:
An unsecured API is essentially a “wide-open backend”2. Foundation of API Design🔹 Core features:
Security must be designed alongside API structure—not added later3. Basic HTTP Authentication (Intro Level)🔹 Rails method:http_basic_authenticate_with name: "admin", password: "secret" 🔹 How it works:
Good for demos ❌
Not safe for production ❌4. Token-Based Authentication with JWTUsing JSON Web Token:🔹 Structure:
JWT is the industry standard for modern APIs5. Why JWT Is More Secure🔹 Advantages:
Security comes from signature verification, not secrecy6. Implementing JWT in Rails🔹 Tool:
The server is the only entity that can generate valid tokens7. Authentication Service🔹 Responsibilities:
Authentication = verifying identity8. Authorization Layer🔹 Implementation:
Authorization = controlling access9. Request Lifecycle with JWT🔹 Flow:
Every request is independently verified (stateless system)10. From Open API to Secure System🔹 Before:
Security transforms your API from public → protectedKey Takeaways
👉 A scalable API architecture
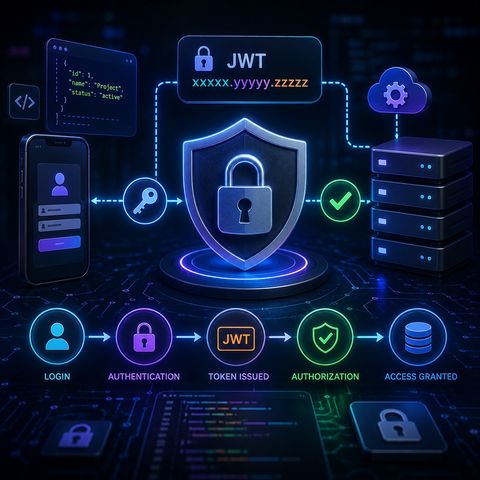
👉 A secure backend for mobile/web appsMental ModelUser logs in → server issues token → client stores token → sends with each request → server verifies → grants/denies access
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
show less
- APIs are publicly exposed endpoints
- Without protection → anyone can access or manipulate data
- Ensure only authorized users can interact with resources
An unsecured API is essentially a “wide-open backend”2. Foundation of API Design🔹 Core features:
- Multiple response formats (JSON)
- Pagination
- API versioning
Security must be designed alongside API structure—not added later3. Basic HTTP Authentication (Intro Level)🔹 Rails method:http_basic_authenticate_with name: "admin", password: "secret" 🔹 How it works:
- Sends username/password with every request
- Credentials sent repeatedly
- Often stored or cached
- Vulnerable if not encrypted
Good for demos ❌
Not safe for production ❌4. Token-Based Authentication with JWTUsing JSON Web Token:🔹 Structure:
- Header
- Payload
- Signature
- Stateless (no server session needed)
- Secure (signed token)
- Scalable
JWT is the industry standard for modern APIs5. Why JWT Is More Secure🔹 Advantages:
- No repeated credentials
- Token can expire
- Cannot be modified without secret key
- Immune to CSRF (no cookies required)
Security comes from signature verification, not secrecy6. Implementing JWT in Rails🔹 Tool:
- JWT Ruby Gem
The server is the only entity that can generate valid tokens7. Authentication Service🔹 Responsibilities:
- Handle signup
- Handle login
- Generate token
- User logs in
- Server validates credentials
- Server returns JWT
Authentication = verifying identity8. Authorization Layer🔹 Implementation:
- Add before_action in controller
- Extract token from headers
- Decode token
- Identify current user
Authorization = controlling access9. Request Lifecycle with JWT🔹 Flow:
- Client sends request with token
- Server validates token
- Access granted or denied
Every request is independently verified (stateless system)10. From Open API to Secure System🔹 Before:
- No identity check
- Full data exposure
- Token required
- User-specific access control
Security transforms your API from public → protectedKey Takeaways
- Basic auth is simple but insecure
- JWT provides stateless, scalable security
- Separate authentication and authorization logic
- Validate every request using tokens
👉 A scalable API architecture
👉 A secure backend for mobile/web appsMental ModelUser logs in → server issues token → client stores token → sends with each request → server verifies → grants/denies access
You can listen and download our episodes for free on more than 10 different platforms:
https://linktr.ee/cybercode_academy
Information

Copyright 2026 - Spreaker Inc. an iHeartMedia Company

Comments